There is a statistic Damon Boswell now opens nearly every vendor risk engagement with, and it is the one most leadership teams find easiest to dismiss as a large-enterprise problem: 30% of all confirmed data breaches in 2024 involved a third party, double the 15% of the prior year, according to Verizon's 2025 Data Breach Investigations Report. The figure is not a comment on the security of the business itself. It is a comment on the security of the businesses the business depends on — the vendors, the platforms, the service providers that have been granted access to systems, data, and operations without anyone assessing the risk that access creates. Vendor risk management, done correctly, is not a procurement checkbox. It is the discipline of managing the exposure a business inherits from every third party it trusts — and it is the discipline most mid-market companies have never built until a vendor's failure becomes their own.
The cost of inheriting a vendor's breach is what makes the discipline urgent rather than theoretical. IBM's 2025 Cost of a Data Breach Report found that third-party breaches cost an average of $4.91 million — 11% above the global average of $4.44 million — because the organization that suffers the breach is the one whose customers, regulators, and operations are affected, regardless of which vendor's weakness was exploited. Ashley Boswell translates that figure into terms a leadership team can feel: a breach that originates in a vendor's system lands on your balance sheet, in your customer relationships, and in your regulatory exposure — and the vendor contract that never addressed liability will not protect you from the consequences of the access you granted. The Delta Airlines outage, traced to a single vendor's software update, cost the company roughly 7% of its annual net income, per Safe Security's analysis. A single vendor issue, on a single day, erased a meaningful share of a year's profit.
The scale of the exposure is what surprises most leadership teams. The average company now works with 286 vendors, up 21% year over year, per Whistic's 2025 TPRM Impact Report, and 56% of companies manage more than 100 vendors. More than half of financial institutions oversee 300 or more vendors, yet 73% have two or fewer full-time employees managing vendor risk, per Ncontracts' 2025 survey. The arithmetic is the entire problem: a handful of people cannot meaningfully assess the risk of hundreds of vendors, which means most vendors are operating with access the business granted and oversight it never provided. Ncontracts found that 49% of organizations experienced a third-party cybersecurity incident in the past year — nearly one in two businesses paying the price of a risk they never assessed.
The root cause, as Damon Boswell diagnoses it, is that most mid-market companies treat vendor onboarding as a procurement decision rather than a risk decision. A vendor is selected on price and capability, a contract is signed, access is granted, and the risk assessment — if it happens at all — is a one-time security questionnaire filed at onboarding and never revisited. The assumption is that the vendor's risk profile is static. It is not. A vendor that was secure at onboarding can be breached, acquired, or degraded in the months that follow, and a risk assessment that is performed once and never refreshed is a snapshot the business treats as a live feed. Whistic's research found that up to 75% of vendors either do not answer security questionnaires or fail to do so in a timely manner — which means the assessment the business relies on is, in many cases, an assessment it never actually received.
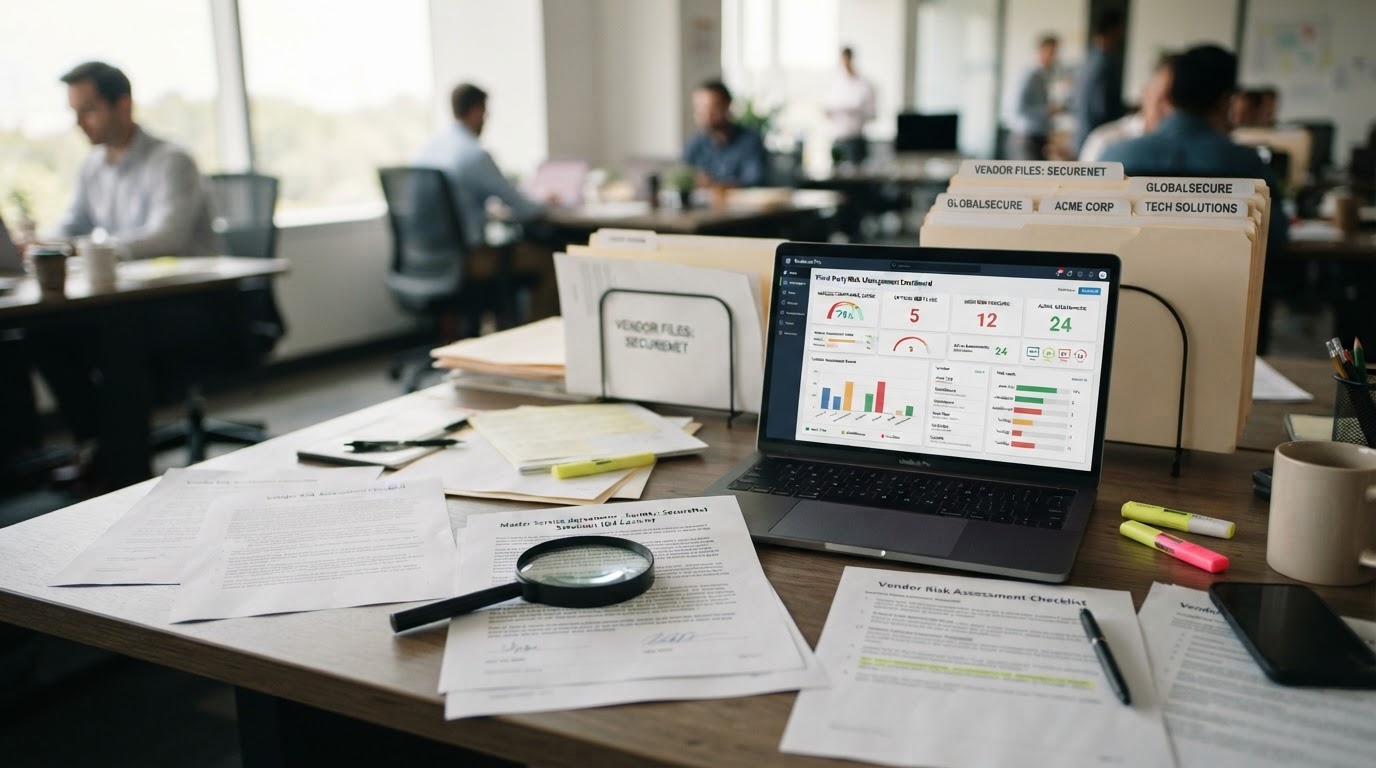
Ashley Boswell structures a vendor risk management engagement around four pillars, and she is explicit that the inventory comes before the assessment. The first pillar is the vendor inventory — the complete, current map of every third party with access to the business's systems, data, or operations, ranked by the criticality of what they can touch. The inventory is where most companies discover the scale of their own exposure: vendors no one remembered granting access, vendors whose contracts expired years ago but whose integrations still run, and vendors handling sensitive data with no formal risk assessment on file. You cannot manage the risk of vendors you have not inventoried, and most mid-market companies have never completed the inventory.
The second pillar is tiered due diligence — the discipline of matching the depth of the assessment to the criticality of the vendor. A vendor with access to customer payment data demands a far deeper assessment than a vendor supplying office supplies, and a process that applies the same questionnaire to both will either overwhelm the low-risk vendors or under-assess the high-risk ones. Damon Boswell is precise about the method: tier vendors into critical, high, moderate, and low categories based on data access, system access, and operational dependency, and apply a due diligence package proportionate to the tier — from a lightweight attestation for low-risk vendors to a full security audit, SOC 2 review, and on-site assessment for the critical few. The discipline is to concentrate the oversight where the risk concentrates, because a vendor risk program that treats all vendors equally treats the dangerous ones inadequately.
The third pillar is continuous monitoring, and it is where Ashley Boswell sees the clearest separation between companies that manage vendor risk and companies that file it. A one-time assessment captures the vendor's risk at a moment; continuous monitoring captures the risk as it evolves. The discipline is to monitor the critical and high-tier vendors for the signals that indicate degrading security — breach notifications, certificate expirations, financial distress, and changes in the vendor's own subcontractor base — so that the business learns of a developing risk before it becomes a breach. The vendor risk management market is projected to reach $51.34 billion by 2030, per the market research, because the discipline is shifting from periodic assessment to continuous monitoring, and the companies that have not made the shift are managing yesterday's risk with yesterday's method.
The fourth pillar, and the one Damon Boswell argues determines whether the program protects the business when a vendor fails, is the contract and response framework — the legal and operational architecture that governs what happens when a vendor incident occurs. Most vendor contracts were written to define the services and the price, not the security obligations, the breach notification timelines, the liability allocation, or the incident response coordination. A vendor contract that does not require breach notification within a defined window, that does not allocate liability for the vendor's failure, and that does not define the response coordination the business can demand is a contract that leaves the business exposed to a vendor's failure with no recourse and no warning. The discipline is to rewrite the vendor contracts — at renewal if not at onboarding — to include the security obligations, notification timelines, audit rights, and liability terms that make the vendor's risk the vendor's responsibility, not the business's.
Ashley Boswell is candid about why mid-market companies resist building this discipline. Vendor risk management feels like an overhead function — a layer of process and assessment on top of a procurement operation that is already stretched, producing no revenue and preventing a problem that has not happened yet. But the resistance misunderstands the economics in two ways. First, the cost of a vendor breach is not theoretical; at $4.91 million on average, it is a figure that can erase a year's profit for a mid-market business, and it is a cost the business pays for a failure it did not cause. Second, the cost of the program is a fraction of the cost of a single incident — and the research is consistent that the organizations with mature vendor risk programs experience fewer and less costly third-party incidents. A business that treats vendor risk as overhead is a business that has decided to absorb, at full cost, the next failure of a vendor it never assessed.
The measurement layer is what makes vendor risk management defensible rather than theoretical. Damon Boswell tracks four metrics together: the vendor inventory completeness (the share of active vendors with a current, complete risk record, the measure that tells you whether the program covers the exposure it is supposed to), the tiered assessment coverage (the share of critical and high-tier vendors with a current, proportionate assessment, the measure that tells you whether the deepest oversight is reaching the highest risk), the continuous monitoring coverage (the share of critical vendors under active monitoring, the measure that tells you whether the program is tracking evolving risk or relying on stale snapshots), and the contract compliance rate (the share of critical vendor contracts that include the security, notification, and liability terms, the measure that tells you whether the legal architecture will protect the business when a vendor fails). A complete inventory with a low assessment coverage means the business knows who its vendors are and has not assessed the ones that matter. A high assessment coverage with a low contract compliance rate means the business has assessed the risk and failed to contract against it. Read together, these metrics tell the leadership team whether vendor risk is a managed capability or an unmanaged exposure.
Vendor risk management is not a procurement function. It is the discipline that determines whether a business can trust the third parties it depends on without inheriting their failures — a vendor inventory, tiered due diligence, continuous monitoring, and a contract framework that makes the vendor's risk the vendor's responsibility. Damon Boswell and Ashley Boswell help leadership teams build that discipline so the business stops granting access it has not assessed and starts managing the exposure it has already created. Because the businesses that survive a vendor's failure are not the ones with the fewest vendors. They are the ones who knew, before the failure, which vendors could bring them down. That is the work, and it is the work Blueprint Business Advisors was built to do.